Security Research
Security Research
4 articles • newest first
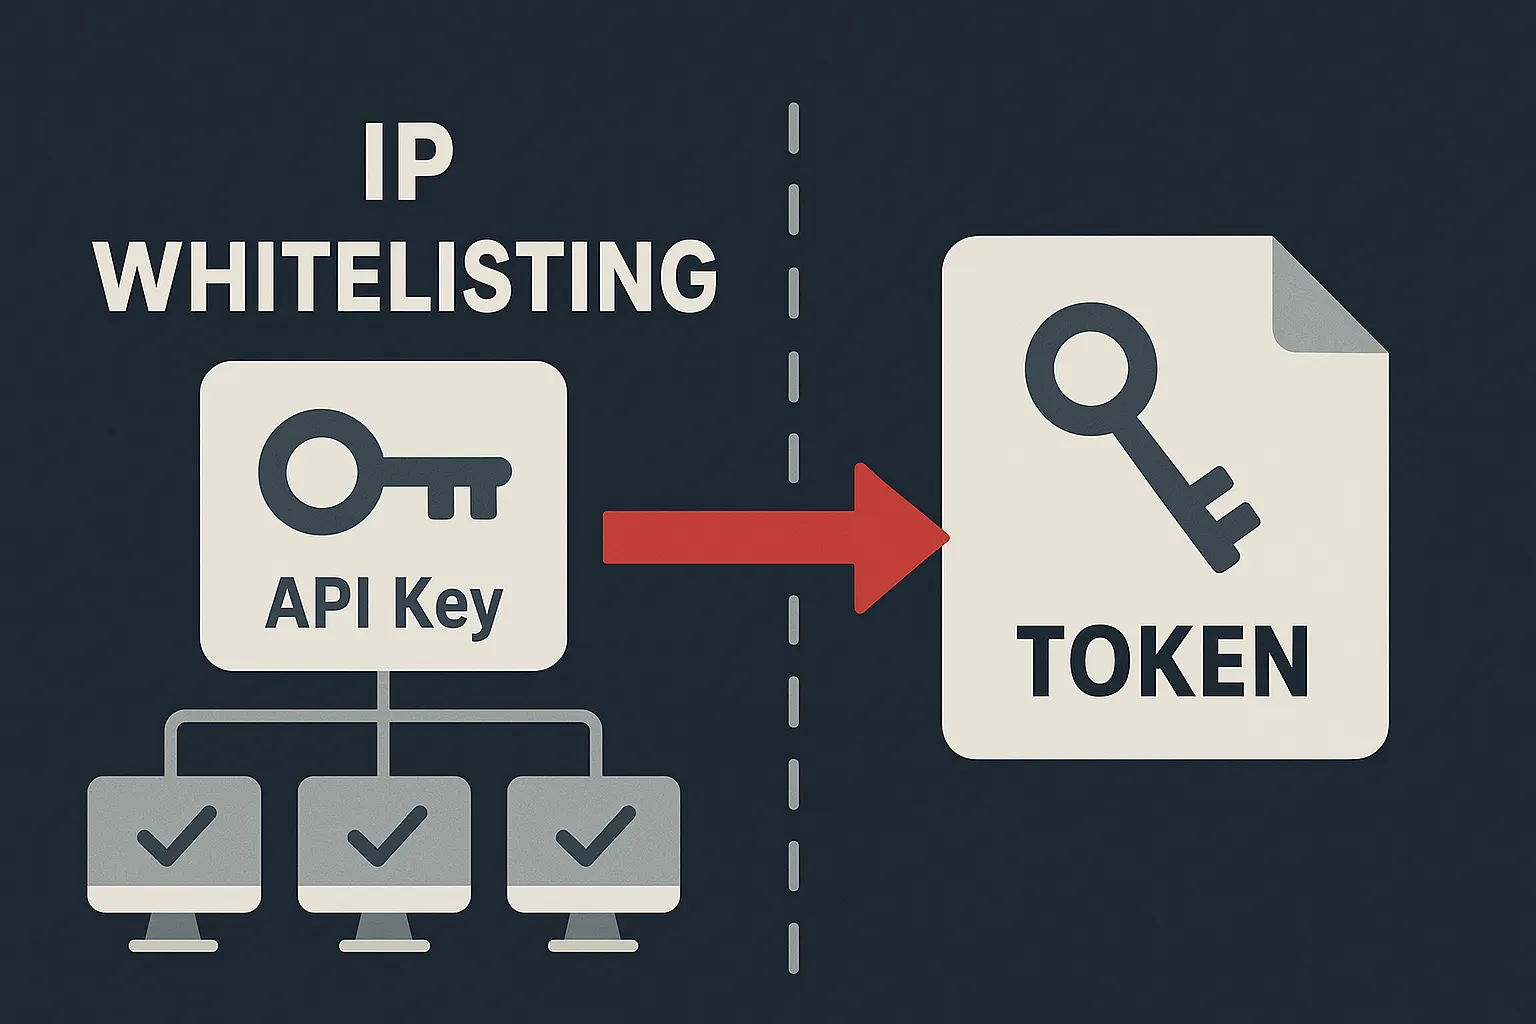
A case study on how Binance's listenKey design bypasses IP whitelisting, why Bugcrowd dismissed it, and what this teaches us about API security in 2025. Update (2026-04-20): This article was original
 Oliver Zehentleitner Oct 7 7 min read
2026-04-29 — A fake recruiter tried to walk me into opening a malicious VSCode workspace.I refused, preserved the artifacts, mapped the infrastructure, and submitted the IOCs to public threat-intel fe
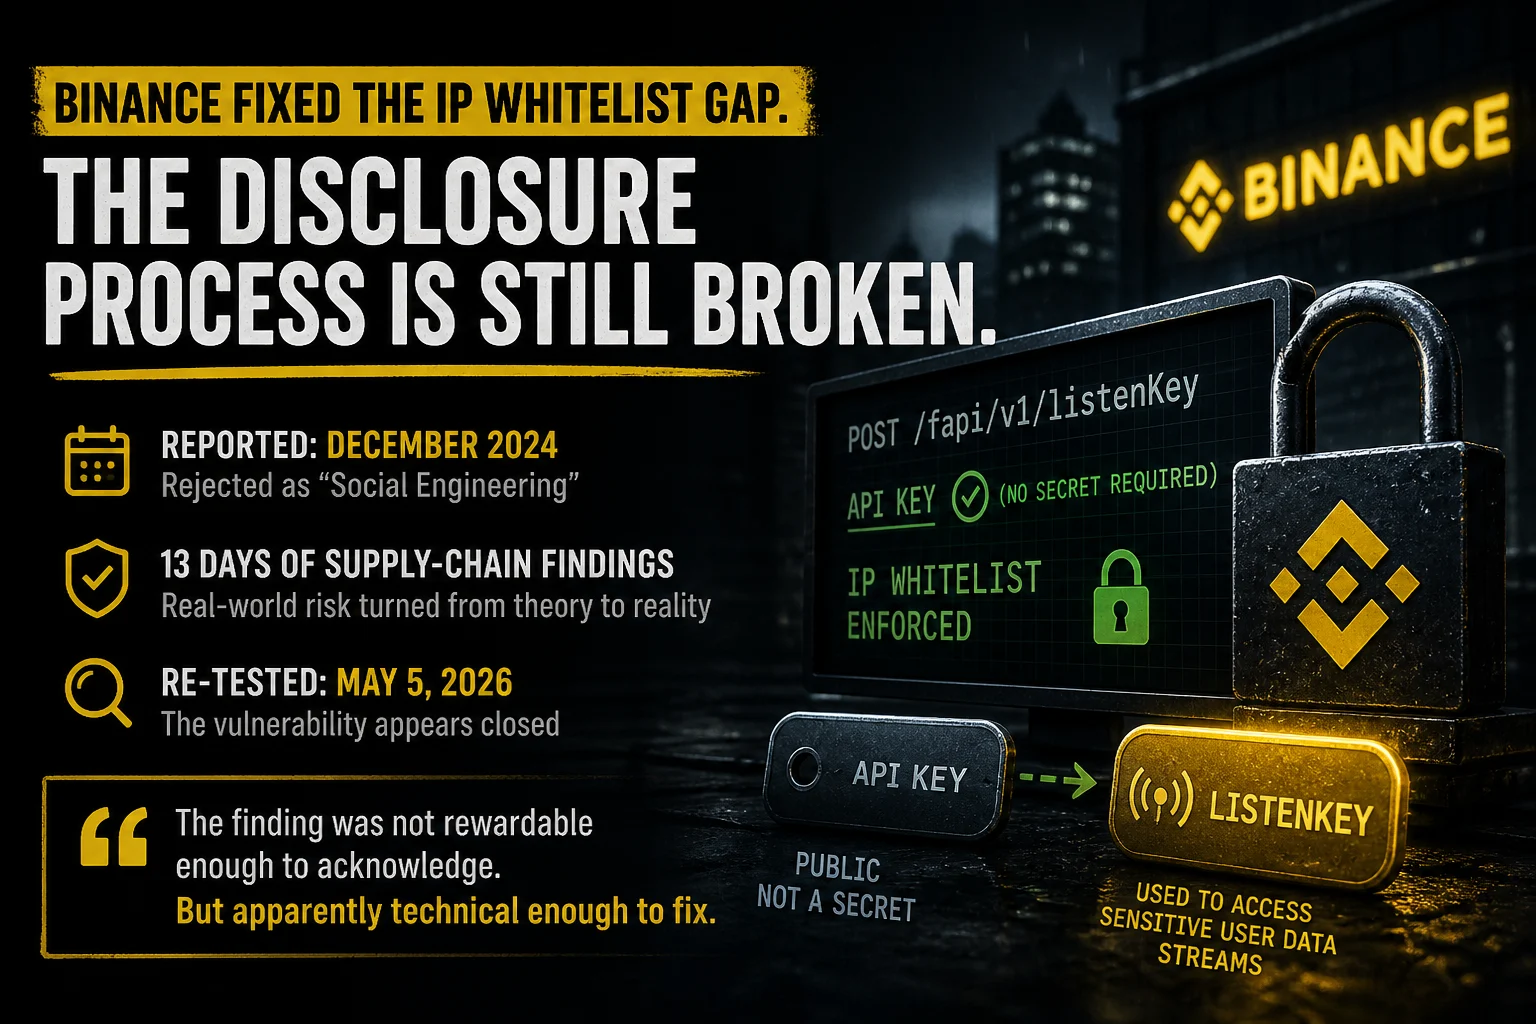
Oliver Zehentleitner Sep 24 12 min readI wanted to re-open an old Binance API security issue. Not because I enjoy re-litigating old reports. Because the last thirteen days made the threat model painfully concrete. I found or stumbled into
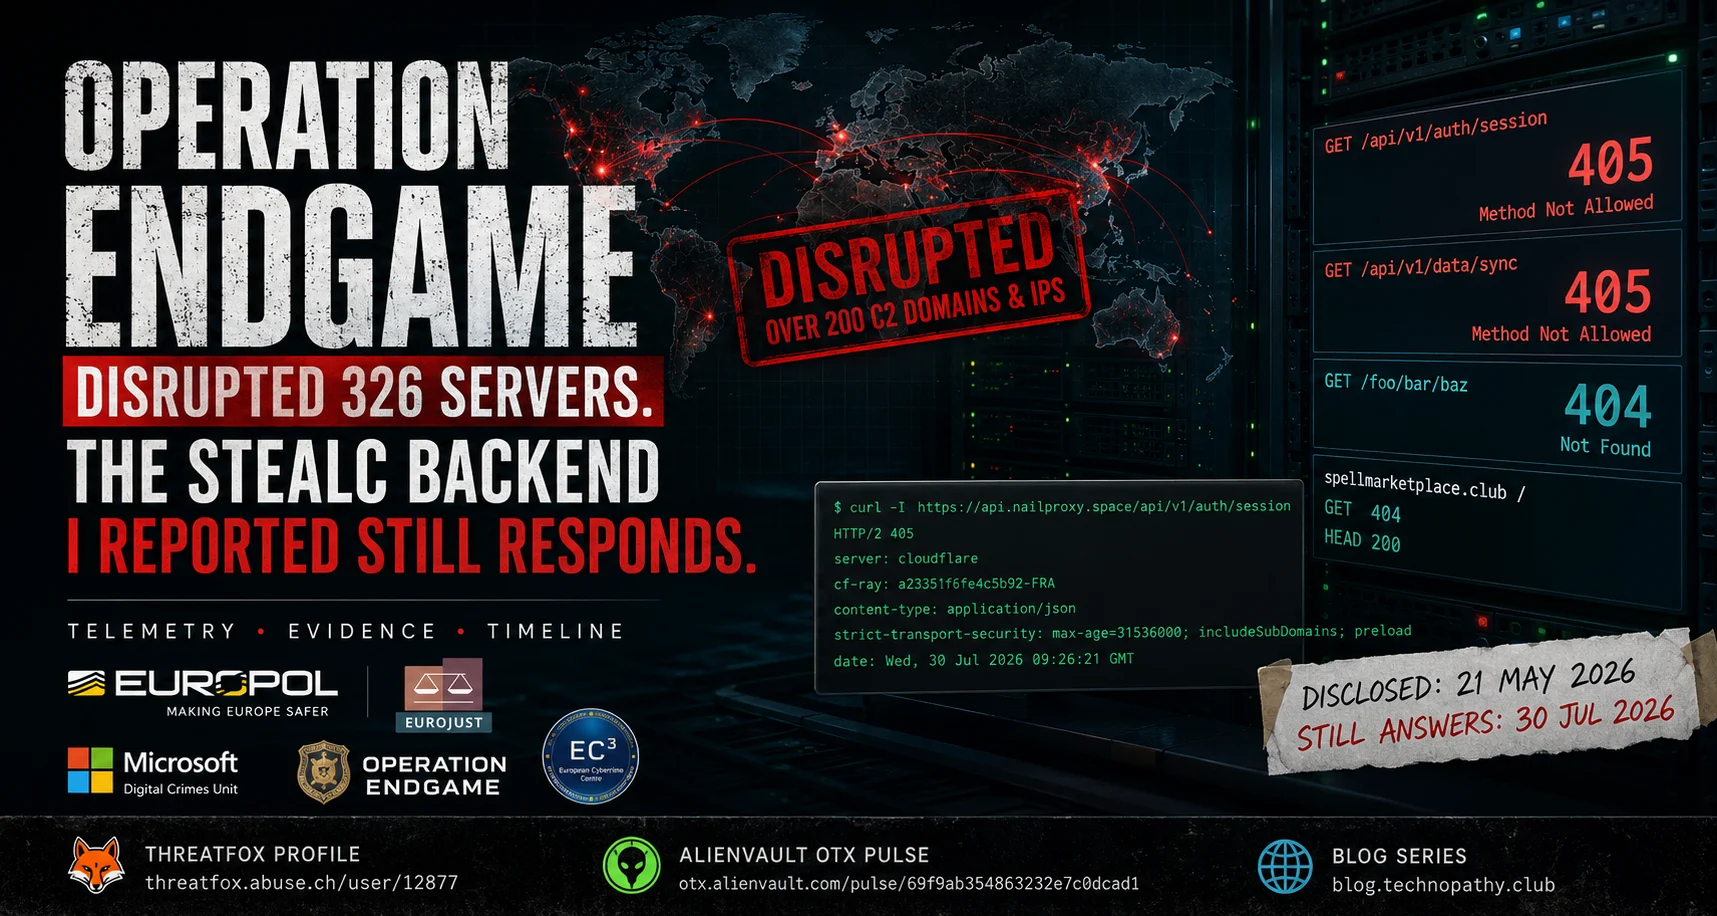
Oliver Zehentleitner Sep 22 8 min readOperation Endgame disrupted 326 servers and 142 domains. Three months after disclosure, the StealC malware routes I documented still respond.
Oliver Zehentleitner Sep 21 11 min read