Are Passkeys a Trap? Fact-Checking a Viral Warning
A Substack post tells everyone to avoid passkeys. I checked it against the specs, vendor docs and NIST guidance. The lock-in worry is real, ...

Oct 12, 2026
4 min
A Substack post tells everyone to avoid passkeys. I checked it against the specs, vendor docs and NIST guidance. The lock-in worry is real, ...
Naive refresh token rotation causes race conditions that randomly log out legitimate users across multiple tabs. Learn how to architect atom...
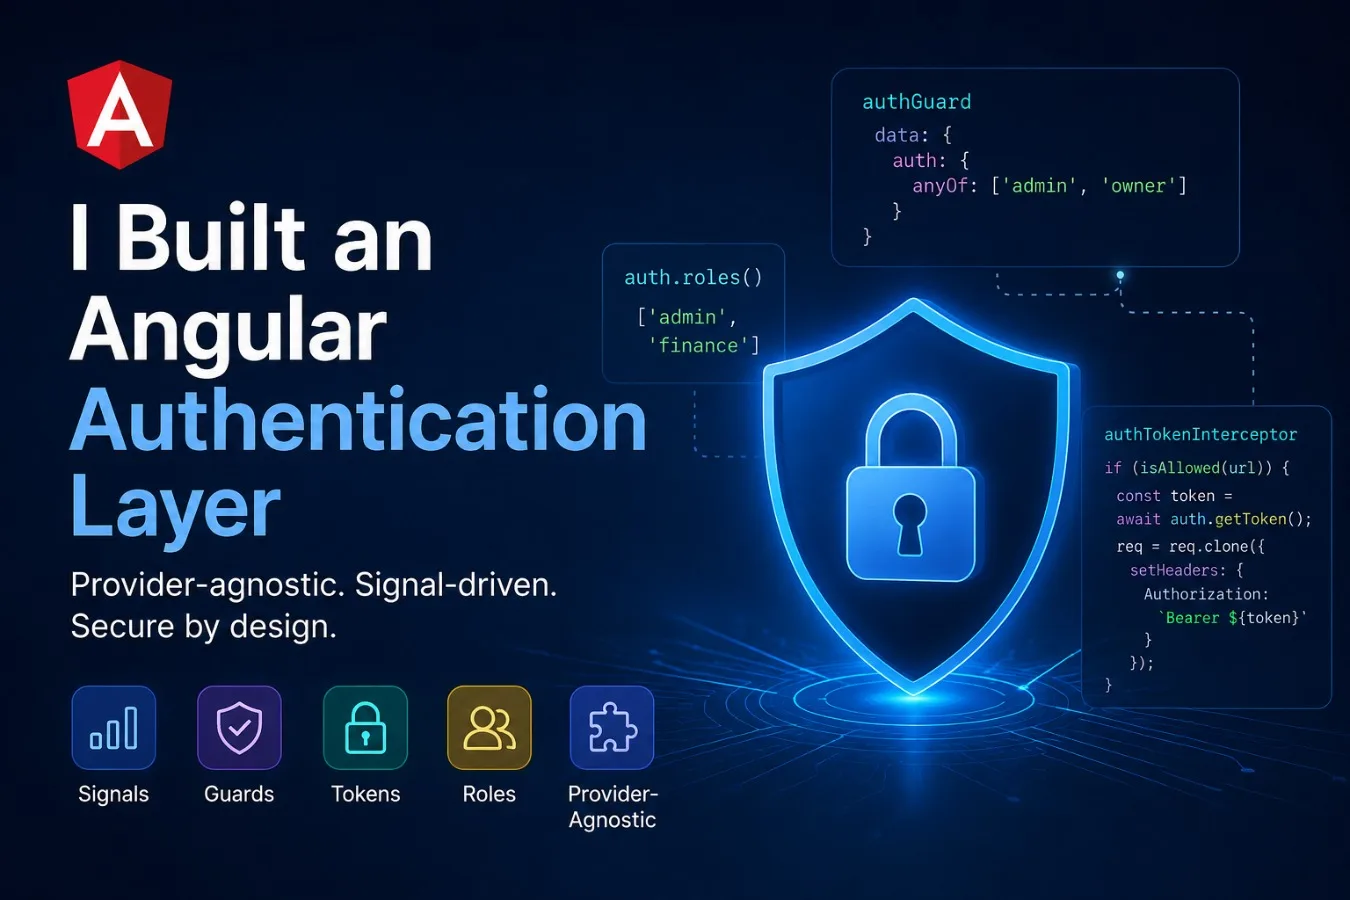
How I designed `ngx-auth-client` around reactive state, provider-agnostic authentication, functional guards, and safer token handling.

A code-first guide to adding WebAuthn passkey registration and login to a NestJS and PostgreSQL API: the schema, the service, the controller...
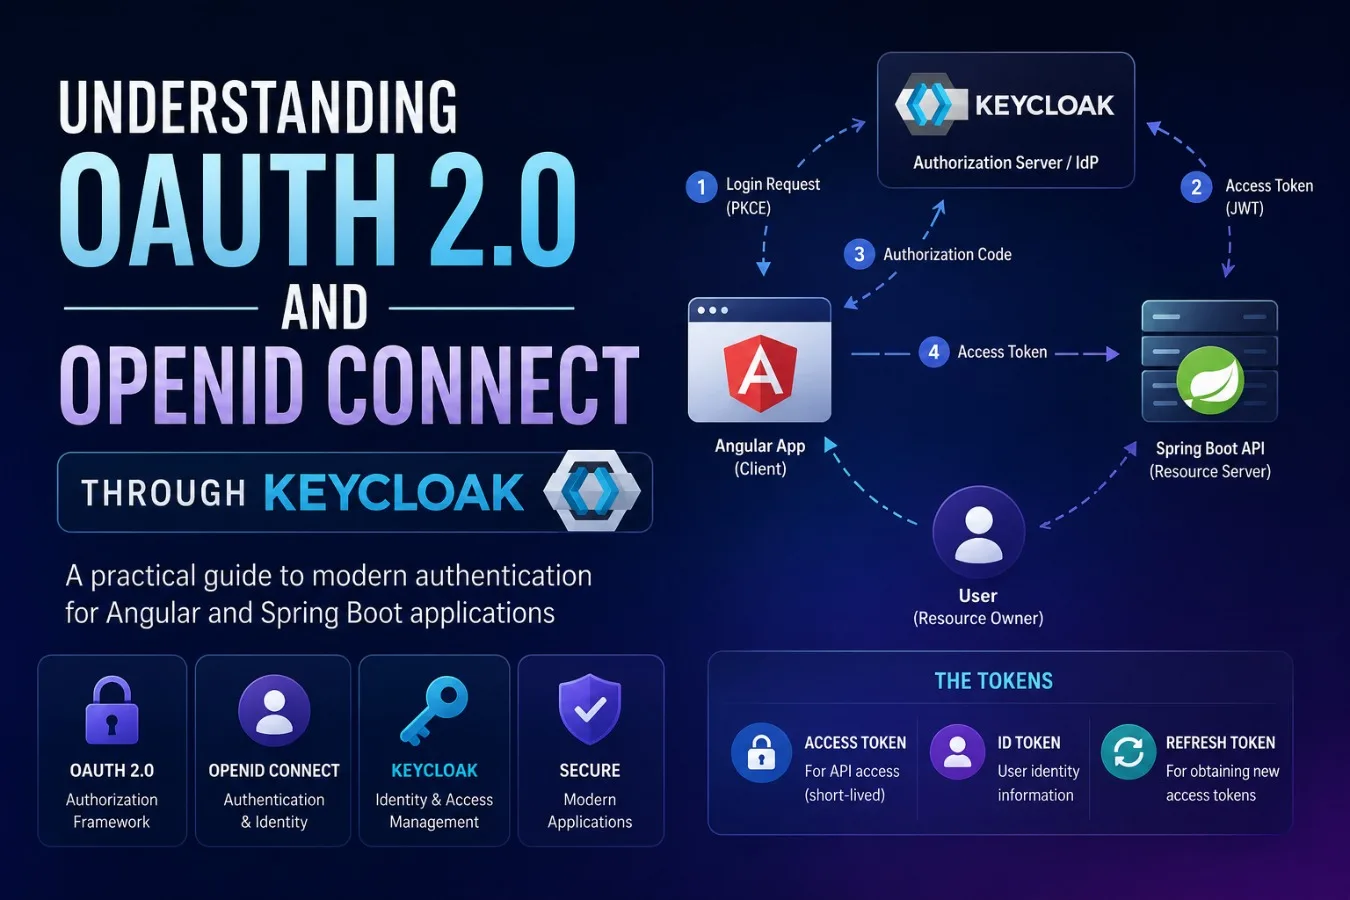
OAuth 2.0, OpenID Connect, JWT, access tokens, refresh tokens, Keycloak. These get mentioned in the same breath so often that they blur into...
Authentication always starts as a login form. Two fields and a button. You could build that in an afternoon, and that afternoon is exactly t...

Learn how to implement Google Sign-In in Node.js without Passport.js by building the complete OAuth 2.0 flow yourself. This guide covers PKC...
A refresh token system where every token is single-use and belongs to a token family. Invalid, expired, and revoked are routine. Reuse means...
Most JWT implementations have at least one critical security flaw. Algorithm confusion, token theft via XSS, missing expiry validation, impr...